PolicyAsCode Blog

Insights and best practices from the policy-as-code community

Latest Post

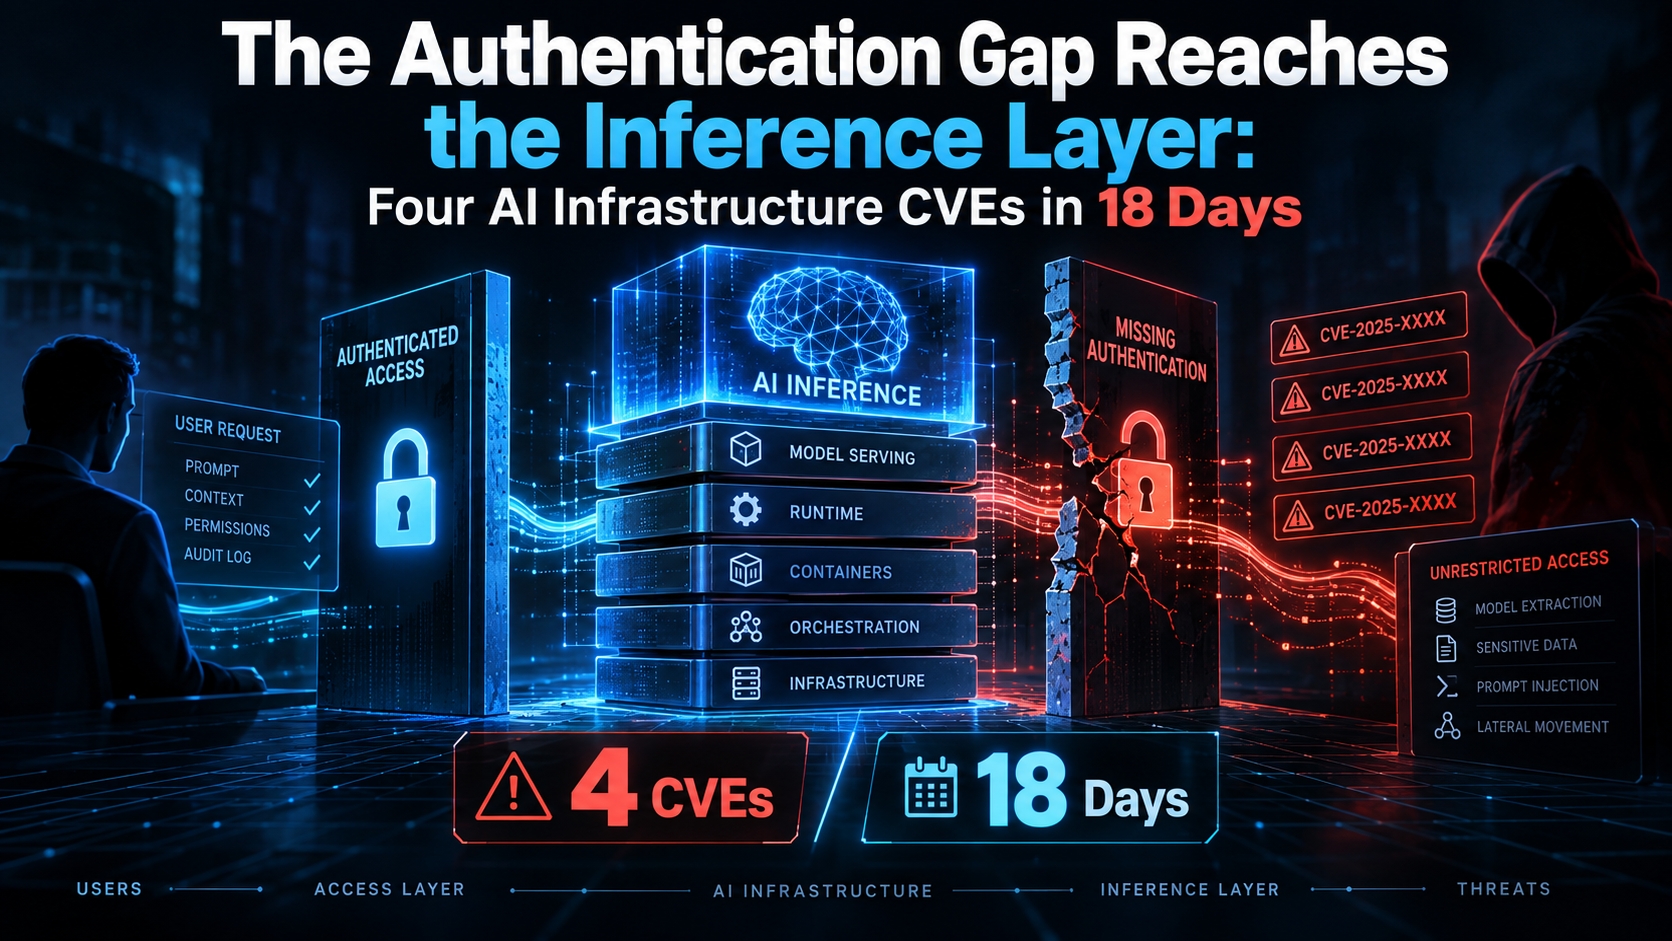
The Authentication Gap Reaches the Inference Layer: Four AI Infrastructure CVEs in 18 Days

Between 25 August and 11 September 2026, four critical CVEs hit NVIDIA NemoClaw, DeepSeek Harness, IBM Langflow and SGLang. Every one traces back to a default configuration, not a model flaw. A verified breakdown of each vulnerability and the policy-as-code controls that actually contain them.

PolicyAsCode September 14, 2026 Vulnerability Analysis
The Authentication Gap Reaches the Inference Layer: Four AI Infrastructure CVEs in 18 Days

Recent Articles

25 posts

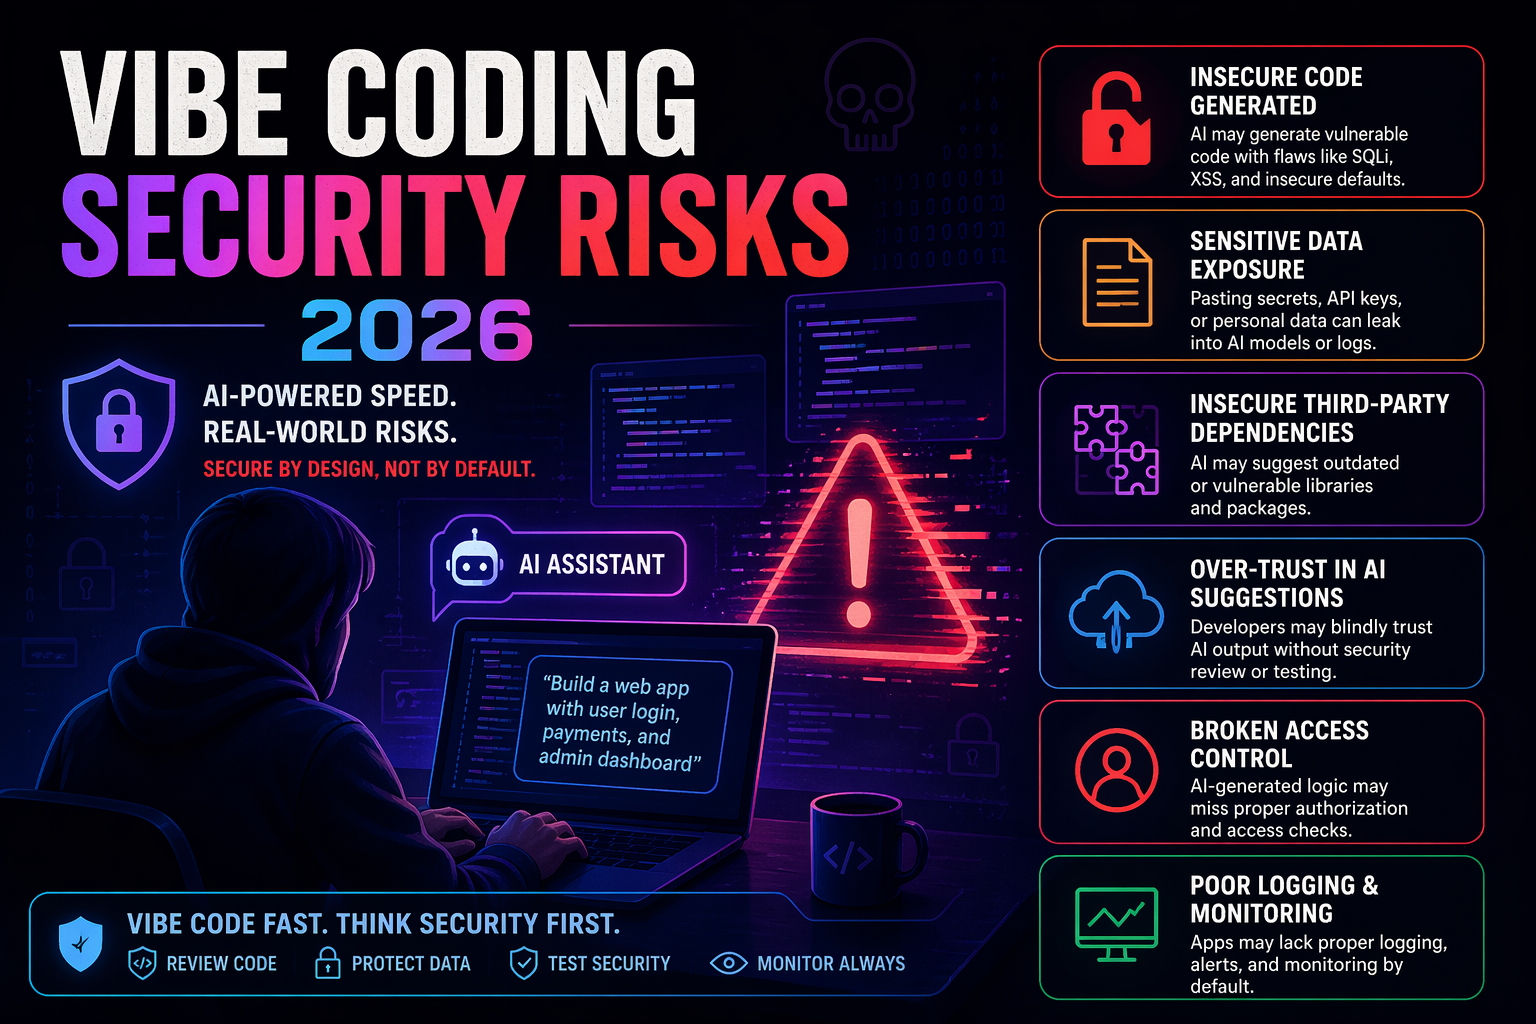
Vibe Coding Is Shipping Vulnerabilities to Production. Here's the Data.

91.5% of vibe-coded apps had at least one vulnerability in Q1 2026. Real incidents — Moltbook, Lovable, Orchids — show what happens when AI-generated code ships without security review. Policy-as-code defenses that actually stop it.
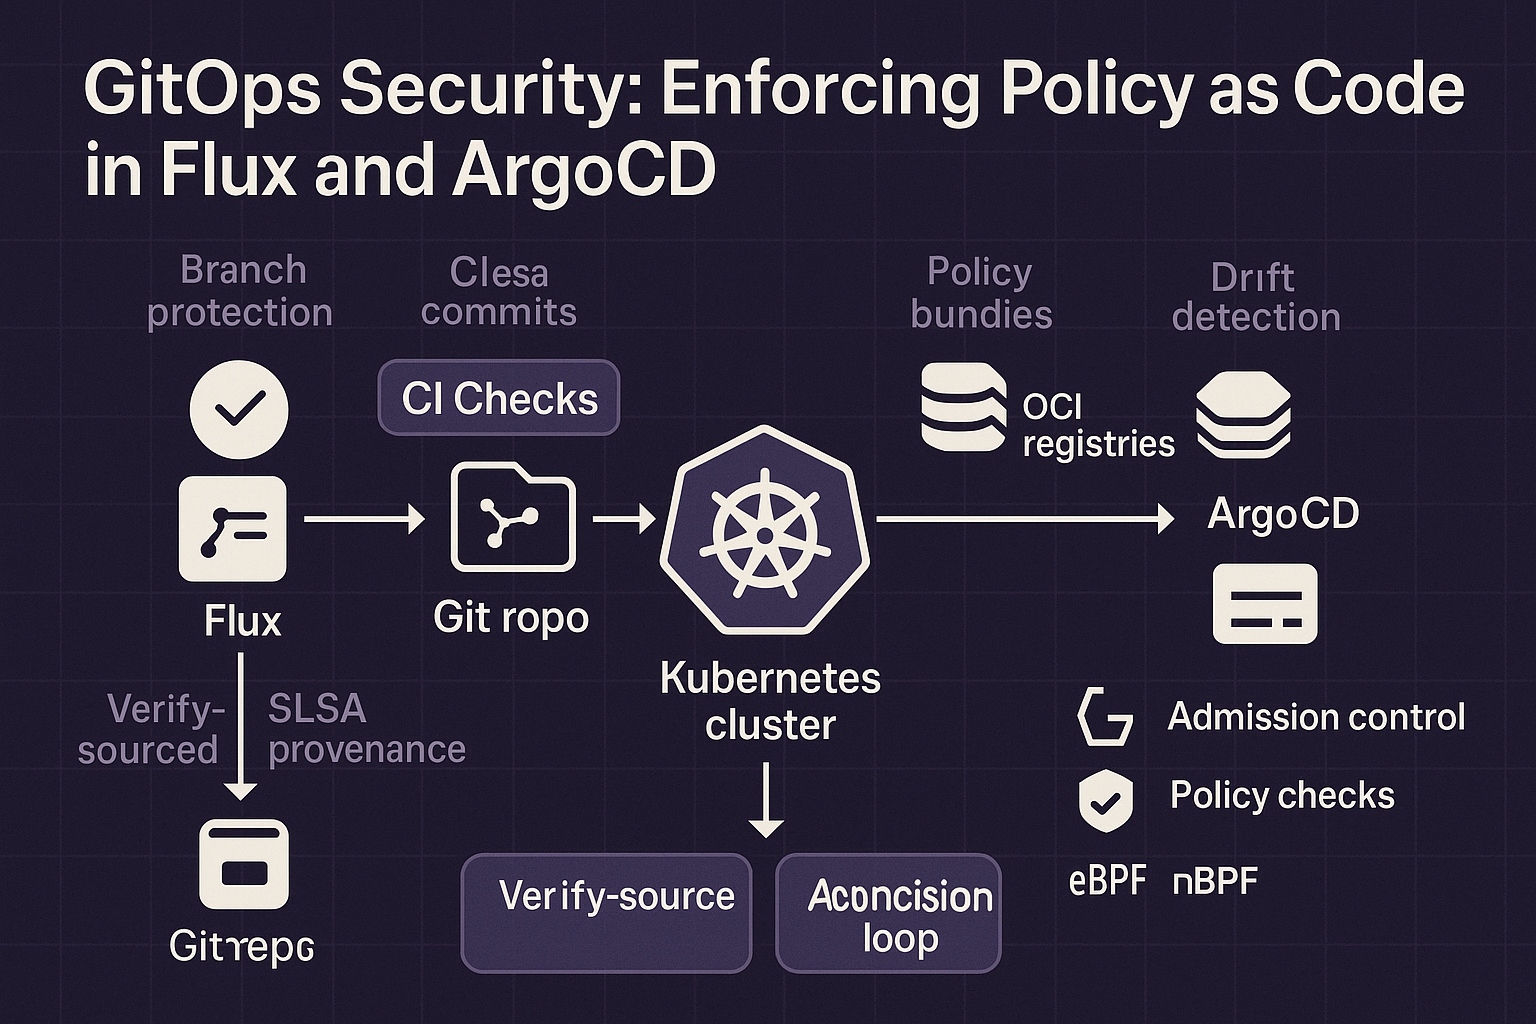
GitOps Security: Enforcing Policy as Code in Flux and ArgoCD

A comprehensive guide to securing GitOps workflows with policy-as-code. Learn how to integrate OPA, Kyverno, and admission controllers with Flux and ArgoCD to prevent misconfigurations, enforce compliance, and automate security at the Git layer.

Explore by Category

Browse articles by topic